Cybersecurity Expert Flagged ECINET Flaws To Poll Body & CERT-In, But Only One Fixed?
Source Entity
Latest News: Todays Latest News Headlines from India & World | Hindustan Times | Hindustan Times
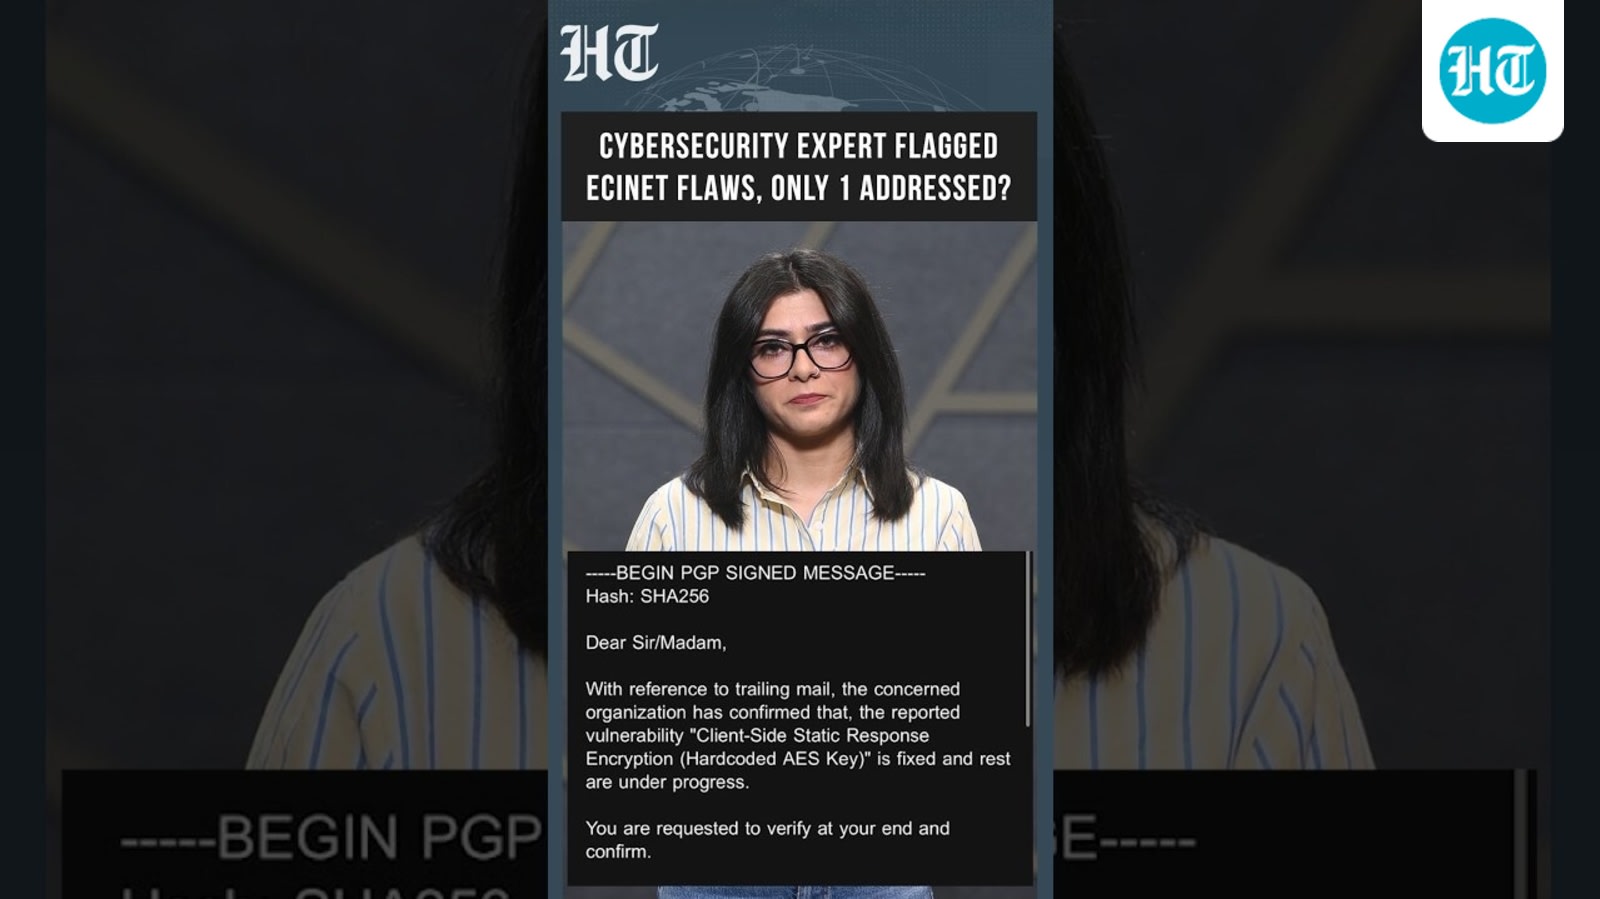
Cybersecurity researcher Nisarga Adhikary reported vulnerabilities in the ECI's ECINET app in July, but only one minor flaw has been addressed after media intervention. While no data breach is suspected, the delayed response from the Election Commission and CERT-In raises concerns regarding institutional cybersecurity protocols.
Cybersecurity Concerns Surrounding the ECINET Platform
Recent reports indicate a significant lapse in the response time between the disclosure of security vulnerabilities and the implementation of patches within the Election Commission of India's (ECI) digital infrastructure. Cybersecurity researcher Nisarga Adhikary identified multiple flaws within the ECINET application and initiated a disclosure process on July 8, contacting both the ECI and the national cybersecurity agency, CERT-In. Despite the critical nature of such disclosures, the response was notably sluggish, spanning over three months.
The Delay and Media Intervention
The situation only gained momentum after the Hindustan Times reached out to the ECI on October 5 for comment. It was only following this media inquiry that CERT-In communicated that a single vulnerability had been addressed. This sequence of events highlights a potential systemic issue in how critical government agencies handle vulnerability reports from independent researchers. The fact that the only resolved issue was the one deemed 'least serious' by the researcher suggests a reactive, rather than proactive, approach to digital security.
The Role of Responsible Disclosure
Responsible disclosure is the cornerstone of modern cybersecurity, where researchers report bugs to organizations to allow for remediation before public exposure. Adhikary followed this standard protocol, yet the lack of timely acknowledgment or action underscores a breakdown in the feedback loop between external security experts and the ECI. While Adhikary has confirmed that no data was stolen or misused, the existence of unpatched vulnerabilities in a system managed by the national poll body presents a significant risk profile.
Institutional Responsiveness and CERT-In
As the nodal agency for responding to computer security incidents, CERT-In's involvement in the remediation process is vital. However, the current status—where the remaining flaws are labeled as 'under progress'—raises questions about the prioritization of these patches. For a system like ECINET, which is integral to election-related processes, the standard for security must be exceptionally high to maintain public trust in digital governance.
Broader Implications for Digital Democracy
As India continues to digitize its electoral processes, the security of platforms like ECINET becomes a matter of national importance. The vulnerability of such systems can impact the integrity of the information they handle. Moving forward, it is essential for the ECI to establish a more transparent and efficient vulnerability disclosure program (VDP). This would ensure that security researchers are not only acknowledged but that their findings are acted upon with the urgency required to protect the integrity of the nation's democratic infrastructure.
Conclusion
While the current situation has not resulted in a data breach, the delay in addressing the reported flaws serves as a cautionary tale. Ensuring robust cybersecurity is an ongoing process that requires constant vigilance, rapid response, and transparent communication. The ECI must prioritize the remediation of the remaining, more severe flaws to ensure that the digital tools used for election management remain secure against potential exploitation.
Verification Required?