Flaw in PHP computer language leads to shutdown of websites around world
Source Entity
Robert Booth and Aisha Down
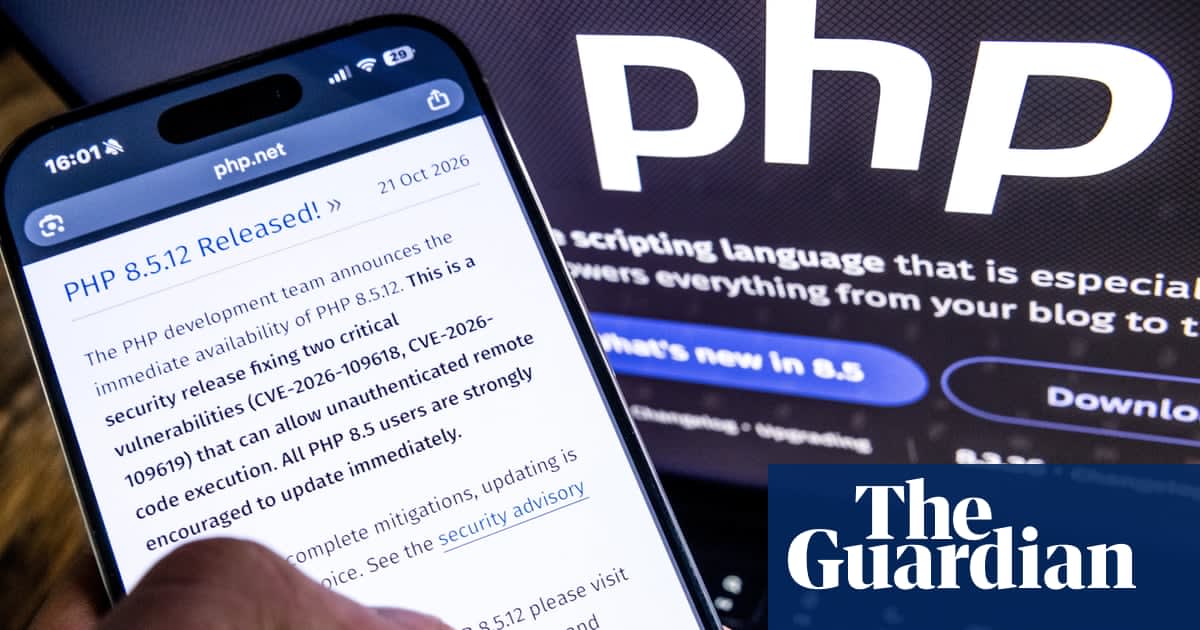
Recent PHP vulnerabilities (CVE-2026-109618 and CVE-2026-109619) have sparked widespread concern, though security experts emphasize they are significantly harder to exploit than previous major vulnerabilities. Cloudflare is currently leveraging AI tools like OpenAI Daybreak and Codex to analyze these risks and accelerate the development of effective defensive patches.
The Complexity of PHP Vulnerabilities (CVE-2026-109618 and CVE-2026-109619)
The cybersecurity community is currently grappling with the emergence of vulnerabilities designated as CVE-2026-109618 and CVE-2026-109619. These flaws, which impact PHP web runtimes, have triggered significant industry attention, leading to a surge in various 'Proof of Concept' (PoC) scripts circulating across platforms like GitHub. These vulnerabilities, often referred to under the umbrella of 'PHP2Shell,' relate to specific request patterns involving HTTP POST methods and PHPSESSID handling, necessitating robust filtering and inspection strategies.
Dispelling the Myth of Ease of Exploitation
Despite the high volume of online activity and alarmist reactions, security experts caution against equating these vulnerabilities with historically devastating exploits such as Log4Shell or Heartbleed. While the underlying flaw is genuine, it is not trivial to weaponize. Current analysis suggests that the majority of publicly available PoC scripts fail to function against a vanilla, standard PHP configuration, indicating that successful exploitation likely requires very specific, non-default environment settings.
The Role of AI in Misinformation and Verification
A concerning trend accompanying this disclosure is the role of Large Language Models (LLMs) in generating potentially misleading exploit code. There is a growing consensus that users are being misled by AI tools that claim to provide functional exploits where none exist. This 'hallucination' of exploitability creates a false sense of urgency and technical risk, complicating the efforts of security teams who must differentiate between genuine threats and noise created by automated tools.
Cloudflare's Proactive Defensive Approach
In response to such complex vulnerability landscapes, infrastructure providers are increasingly turning to AI for defense. Cloudflare, for example, is utilizing OpenAI Daybreak to investigate these specific vulnerabilities and propose actionable fixes for human review. Furthermore, by employing tools like Codex, developers are not only speeding up the remediation process but also improving the overall quality and security of the patches being deployed to the network edge.
Future Trends in Vulnerability Management
As we look forward, the lifecycle of vulnerability disclosure is clearly shifting. The combination of automated threat detection using AI and the increased scrutiny required to validate PoC scripts suggests a future where defensive speed will rely heavily on machine-assisted analysis. Moving away from reactive, manual patching toward AI-driven investigation will become the standard for maintaining the integrity of web runtimes like PHP in an increasingly complex threat environment.
Conclusion
While CVE-2026-109618 and CVE-2026-109619 present a technical challenge, they serve as a critical reminder of the importance of skeptical security analysis. By leveraging advanced tooling while maintaining a rigorous, evidence-based approach to vulnerability validation, the industry can better defend against these sophisticated threats without succumbing to the panic induced by unverified, AI-generated exploit claims.
Multiple Citing Sources