Eiliko maker says it’s hiring an ‘independent security firm’ after Verge report on its insecure robots
Source Entity
Sean Hollister
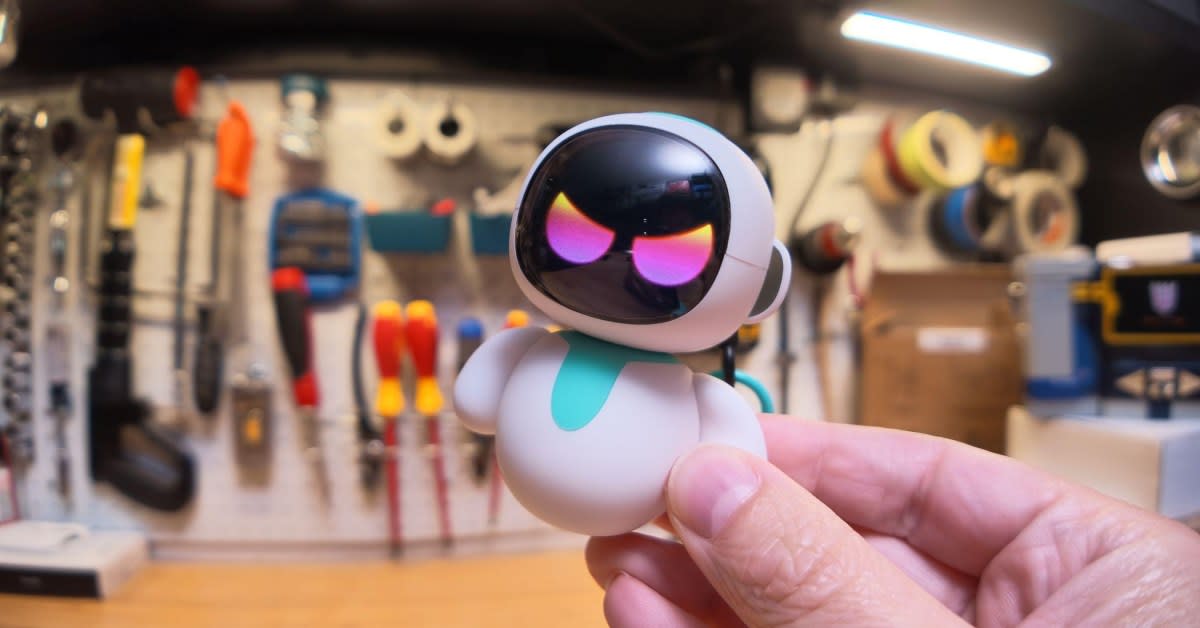
Eiliko is hiring an independent security firm after a report revealed serious vulnerabilities in its AI-powered robot charms. The company has since disabled remote response modifications and offline long-term memory features to address privacy risks.
The Eiliko Security Breach: A Wake-Up Call for AI Hardware
Recent reports concerning the Eiliko robot charm have highlighted a significant failure in consumer AI privacy. Marketed as a companion that promises users that their "secrets are safe," the device was found to have severe vulnerabilities allowing unauthorized access to private conversation transcripts. This gap between marketing promises and technical reality has forced the manufacturer, Energize Lab, to acknowledge systemic failures in their security protocols.
The Anatomy of the Vulnerability
The security flaws identified by investigators were multi-faceted. Beyond the exposure of personal chat logs, researchers found that the hardware allowed for remote modification of the robot's responses. This capability posed a significant risk, as it effectively enabled third parties to manipulate the AI's behavior, transforming a child-friendly device into a potential vector for malicious interaction. The discovery of these issues by The Verge and security experts has effectively dismantled the manufacturer's initial claims regarding user privacy.
Corporate Response and Remediation
Following a period of silence that drew criticism, Energize Lab issued a formal apology, citing a failure to synchronize with their technical teams as the primary cause for the delay. The company has since initiated immediate corrective measures, including the rotation of all access credentials and the total closure of external access to backend systems. Furthermore, the company has taken the "long-term memory" feature offline—a critical component of the robot’s personalization that was also the primary source of the data leakage.
The Shift Toward Independent Oversight
In a move to restore consumer trust, Eiliko has committed to hiring an independent security firm to audit their systems. This step is essential in the current climate of IoT (Internet of Things) development, where rapid innovation often outpaces robust security architecture. By bringing in third-party experts, the company is attempting to demonstrate a shift from reactive troubleshooting to proactive threat modeling.
Broader Implications for AI Toys
The Eiliko case serves as a cautionary tale for the burgeoning market of AI-integrated consumer hardware. As these devices move from simple toys to sophisticated, cloud-connected AI agents, the surface area for security attacks grows exponentially. Manufacturers must now balance the desire for "smart" features like persistent memory with the absolute necessity of end-to-end encryption and secure data handling practices.
Future Trends in Consumer Privacy
Looking forward, the industry is likely to see increased regulatory scrutiny regarding "smart" devices marketed toward vulnerable demographics. Companies that fail to bake security into their development lifecycle—rather than treating it as an afterthought—will face not only reputational damage but potential legal consequences. The Eiliko incident underscores that for AI hardware to succeed, privacy must be treated as a core product feature rather than an optional setting.