Fake nuclear warnings in Ukraine as Moscow, Kyiv report separate cyberattacks on emergency apps
Source Entity
US Top News and Analysis
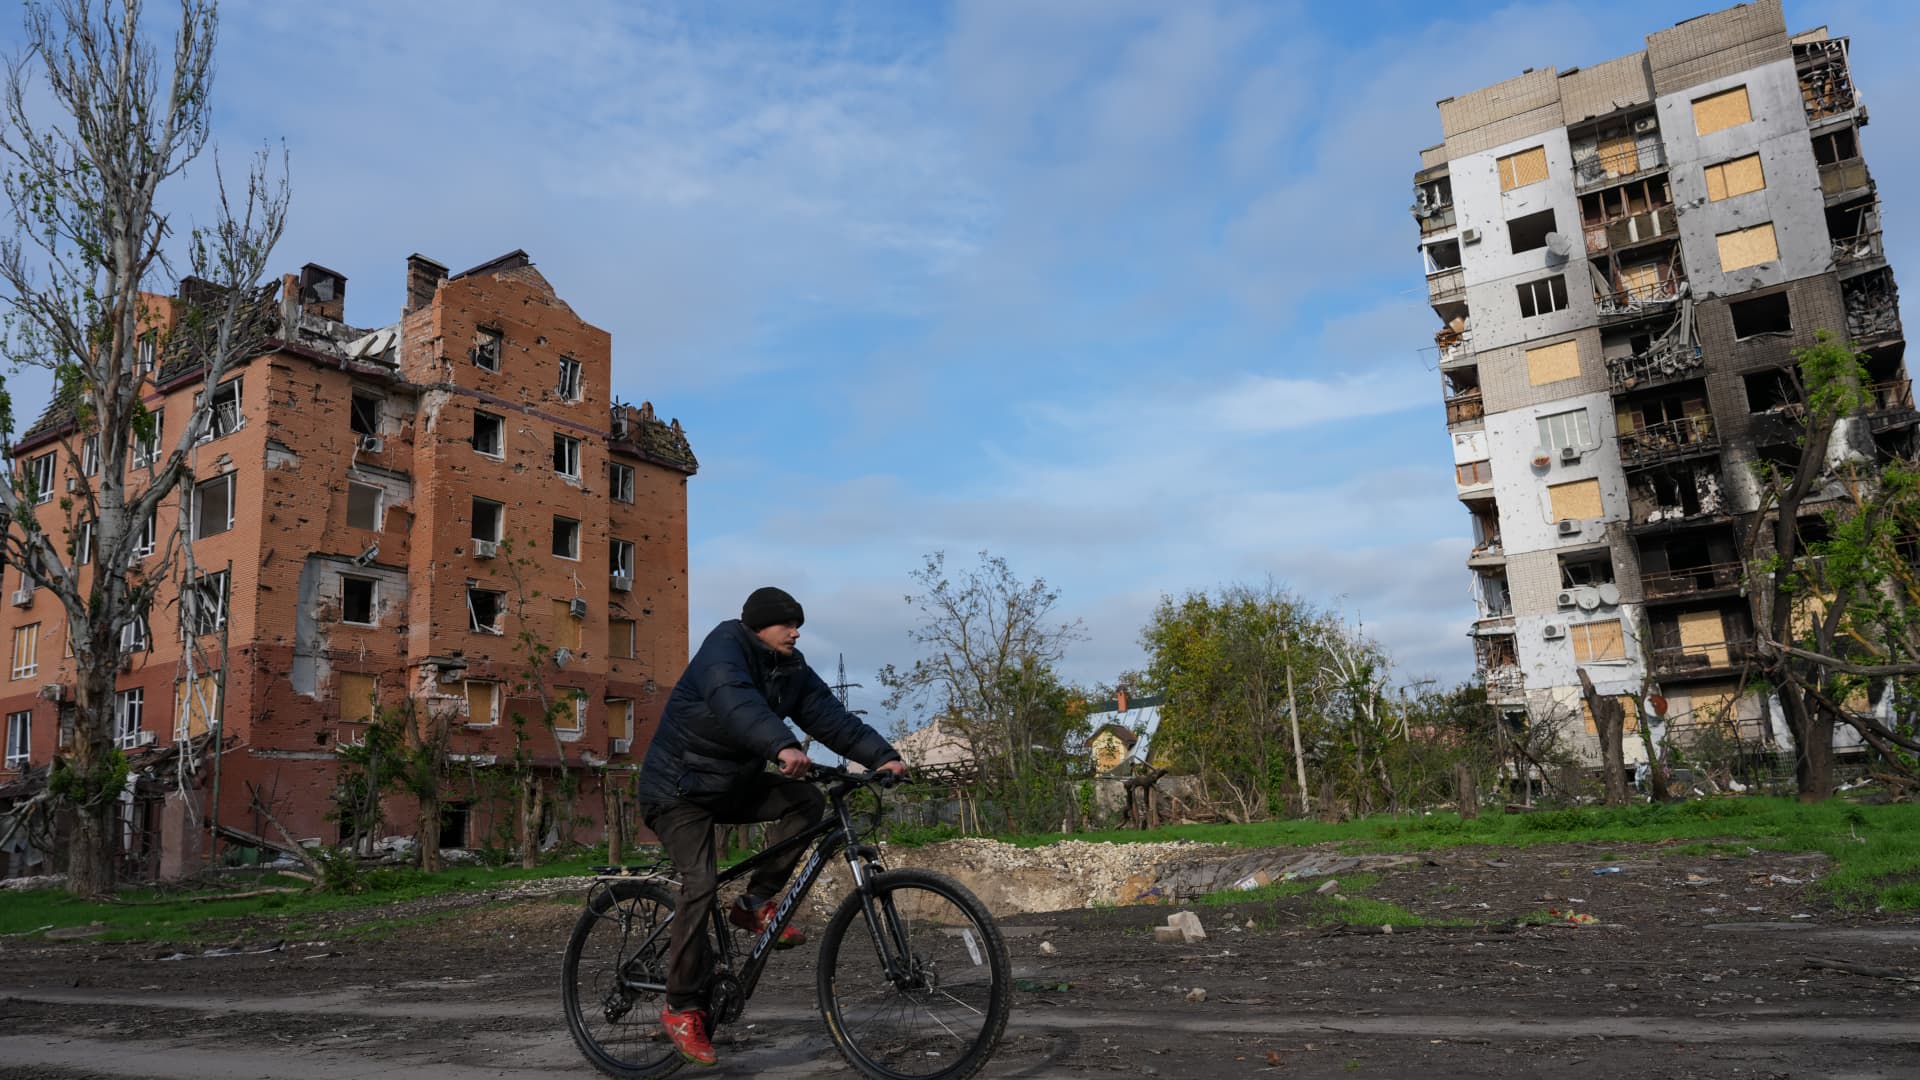
Ukraine and Russia both reported cyberattacks on their emergency alert applications, which pushed false warnings of nuclear and chemical threats. Authorities in both nations quickly debunked the alerts and urged citizens to rely on official government channels.
Cyber Warfare Escalates: The Weaponization of Emergency Alerts
In a concerning development in the ongoing conflict, both Ukraine and Russia have reported significant cyberattacks targeting their respective national emergency alert mobile applications. These platforms, designed to provide life-saving information during active combat, were compromised to disseminate false warnings regarding nuclear and chemical threats, as well as fabricated reports of street-level hostilities. The incident highlights a critical vulnerability in the digital infrastructure used to protect civilian populations during times of war.
The Breach of Ukraine's Air Alarm App
On Sunday, the Ukrainian Air Force confirmed that its 'Air Alert' application—a vital tool for millions—had been subjected to unauthorized interference. Users in Kyiv and other regions suddenly received alarming notifications warning of radiation leaks and chemical incidents. The Air Force acted swiftly to mitigate panic, using their official Telegram channel to verify that the notifications were fraudulent and that no such threats existed. The incident forced a temporary suspension of push notifications, effectively blinding a critical safety mechanism during a period of heightened regional volatility.
Reciprocal Attacks on Russian Infrastructure
Shortly after the Ukrainian breach, Russia’s Ministry for Emergency Situations reported that its own mobile application had fallen victim to a massive cyberattack. Attackers utilized the platform to broadcast fake information to the public, echoing the pattern observed in the Ukrainian incident. While the specific attribution of these attacks remains under investigation, the near-simultaneous nature of these digital strikes suggests a coordinated effort to erode public trust in official government communication channels and induce psychological distress among civilian populations.
The Strategic Objective: Psychological Warfare
Beyond the technical failure, the primary objective of these cyberattacks appears to be the weaponization of fear. By injecting false nuclear and chemical warnings into the daily lives of citizens, the perpetrators aim to create chaos, overwhelm emergency services, and destabilize the morale of the populace. In a war defined as much by narrative and perception as by physical territory, the ability to manipulate the information ecosystem is a potent, albeit dangerous, tactical advantage.
The Future of Digital Civil Defense
This event serves as a stark reminder of the fragility of centralized digital defense systems. As cyber warfare becomes increasingly integrated into conventional military operations, the need for hardened, multi-layered verification protocols has never been greater. Moving forward, both nations and international observers must grapple with the challenge of securing these platforms against sophisticated actors who view public panic as a legitimate strategic outcome. Relying on redundant, decentralized communication channels remains the most effective defense against such digital incursions, as emphasized by Ukrainian authorities following the breach.
Conclusion
While the situation was contained without physical harm, the successful infiltration of critical emergency infrastructure marks a disturbing escalation. As the conflict continues, the resilience of information systems will remain a key focal point for both cyber-defenders and those seeking to exploit the digital landscape for strategic gain.
Multiple Citing Sources