Hacking the Xbox 360 Hypervisor Part 3: Bad Update Improvements
Source Entity
Hacker News
Security researchers have significantly optimized the 'Bad Update' Xbox 360 hypervisor exploit, boosting its efficiency from a 30% success rate to near-instantaneous execution. This development marks a critical milestone in the ongoing reverse-engineering efforts targeting legacy console security.
The Evolution of Xbox 360 Hypervisor Exploitation
The release of the third installment in the 'Hacking the Xbox 360 Hypervisor' series highlights a significant leap in the technical maturity of legacy console exploitation. Initially, the 'Bad Update' proof-of-concept (PoC) was a cumbersome tool, requiring approximately 20 minutes to execute with a success rate of only 30%. By refining the underlying mechanics of the exploit, researchers have transformed it into a near-instantaneous process with a success rate approaching 100%, demonstrating how collaborative community efforts can rapidly evolve rudimentary security research into highly reliable exploits.
Refining the 'Bad Update' Mechanism
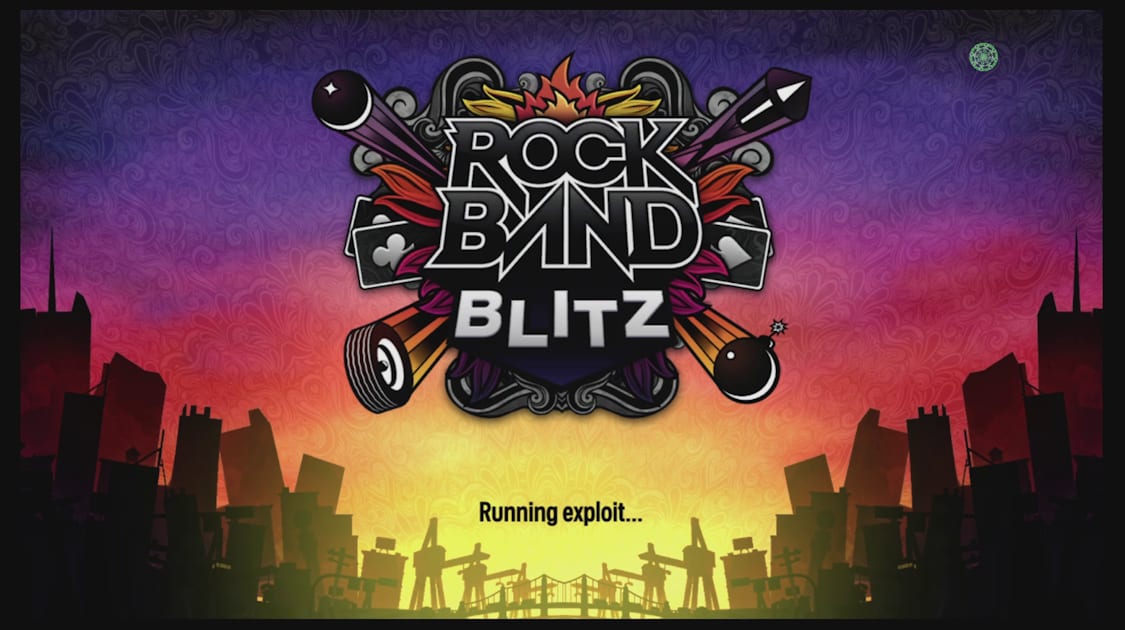
The transition from a sluggish, unreliable PoC to a polished exploit underscores the importance of iterative development in the security research community. The original 'Bad Update' v1.0 served as the foundation, but it was the subsequent contributions from researchers such as “ihatecompvir” and “InvoxiPlayGames” that truly unlocked the exploit's potential. By discovering new entry points—specifically within the demo version of Rock Band Blitz—these contributors successfully bypassed existing limitations, allowing for a more streamlined interaction with the hypervisor.
The Role of Community Collaboration
This progression serves as a quintessential example of open-source security research. Unlike corporate-led bug bounty programs, the Xbox 360 scene relies heavily on the collective intelligence of enthusiasts who document their findings in blog series. The fact that this optimization occurred in the months following the initial release of the PoC illustrates how shared knowledge acts as a catalyst for innovation. Each researcher builds upon the work of their predecessor, turning minor findings into significant security breakthroughs.
Technical Implications for Legacy Hardware
The Xbox 360's hypervisor was once considered a robust security boundary. However, as the console reaches its end-of-life cycle, the focus of the community has shifted toward fully understanding and dismantling these legacy protections. The 'Bad Update' exploit is not merely a tool for customization; it represents a fundamental breakdown of the trust model the hardware originally relied upon. By achieving near-instantaneous execution, these researchers have effectively rendered the initial hypervisor security measures obsolete.
Future Trends and Peer Pressure
Looking ahead, the narrative set by this blog series suggests that the landscape of Xbox 360 exploitation is far from static. The upcoming discussion regarding the 'peer pressure' exploit, as teased by the author, indicates that researchers are moving toward even more sophisticated methods of bypassing system-level security. This ongoing research ensures that the history of the Xbox 360 will remain a primary case study for security professionals interested in the cat-and-mouse game of console hardware protection.
Conclusion
The rapid improvement of the 'Bad Update' exploit is a testament to the dedication of the Xbox 360 homebrew and security community. By turning a 20-minute, hit-or-miss process into an efficient, near-instantaneous utility, researchers have not only enhanced their own toolkits but have also provided deep insights into the vulnerabilities of the console's architecture. As the community moves toward future exploits like 'peer pressure,' the legacy of the Xbox 360 continues to be defined by the relentless pursuit of total system control.