Not cool: who hacked France’s supermarket fridges?
Source Entity
Kim Willsher in Paris
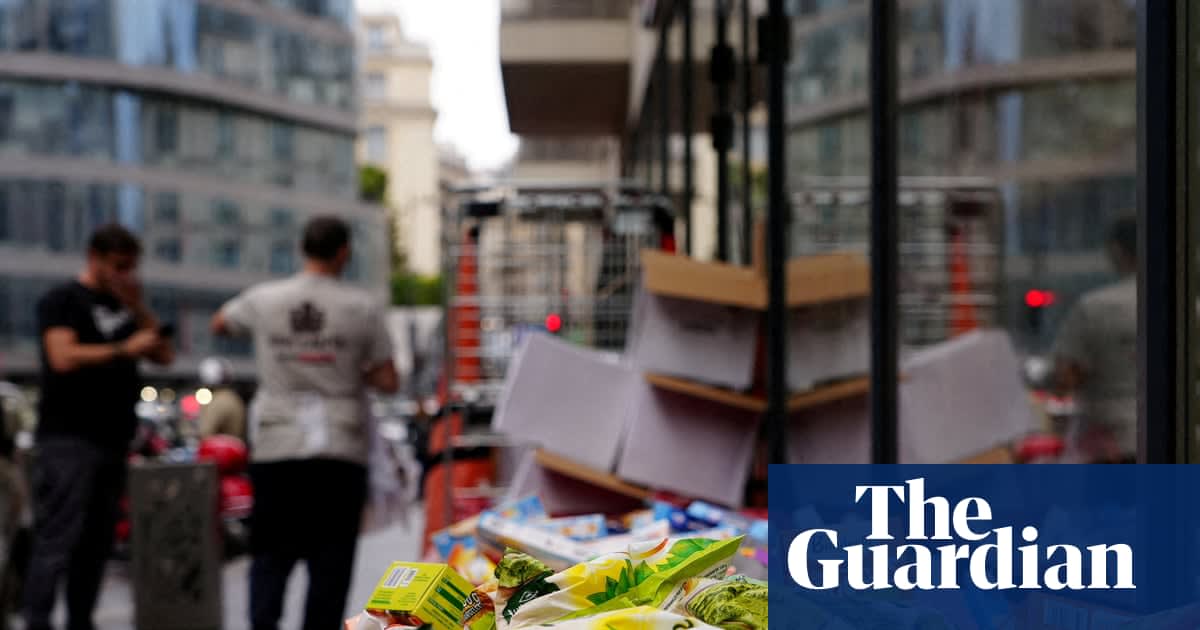
A sophisticated cyber-attack on French supermarket cooling systems caused widespread food spoilage and safety hazards. Hackers remotely manipulated temperatures to extreme levels, prompting significant concerns regarding critical infrastructure security.
The Weaponization of Industrial IoT: A New Frontier in Cyber-Warfare
Last Sunday, the French retail sector faced a chilling demonstration of the vulnerability inherent in modern, interconnected industrial systems. In a highly unusual and disruptive cyber-attack, the digital thermostats governing refrigeration units in supermarkets across the country were compromised. By remotely overriding the operational parameters of thousands of chiller cabinets and freezers, attackers successfully destabilized the cold chain, turning essential food storage infrastructure into a liability.
The Mechanics of the Breach
The scale of this incident was significant, occurring in the late-night hours when oversight is typically minimal. Attackers manipulated temperature setpoints from sub-zero conditions, such as -27C, to extreme heat exceeding 50C and, in some reported cases in Normandy, as high as 80C. This rapid transition essentially transformed industrial cooling units into ovens, leading to the rapid defrosting and subsequent degradation of perishable goods. The physical impact was immediate, with shop staff encountering blast-furnace conditions upon their arrival the following morning.
Escalating Physical Consequences
Beyond the direct loss of inventory, the incident manifested severe physical risks. The extreme heat generated by the forced operation of these cooling units was sufficient to spark internal fires, triggering automatic sprinkler systems and causing collateral water damage to store premises. This evolution from a digital breach to a physical safety hazard represents a dangerous escalation in the tactics employed by threat actors, moving beyond mere data theft or service disruption into the realm of potential physical destruction.
Vulnerabilities in the Cold Chain
The attack underscores a critical failure point in modern supply chain management: the reliance on Internet of Things (IoT) connectivity for temperature monitoring and control. While these systems provide efficiency and real-time data analytics, they also offer a wide attack surface for malicious actors. When these systems are not adequately segmented from public-facing networks or secured with robust authentication, they become prime targets for state-sponsored entities or rogue hackers seeking to inflict economic damage and chaos.
Broader Implications for Global Security
This event is a stark reminder that as physical infrastructure becomes increasingly 'smart,' it also becomes increasingly fragile. The ability to manipulate the environment within a supermarket suggests that similar logic could be applied to broader industrial control systems, including water treatment plants, power grids, or pharmaceutical storage facilities. The 'unprecedented' nature of this attack suggests that existing cybersecurity frameworks in the retail sector may be insufficient to defend against adversaries capable of manipulating industrial hardware.
Future Trends and Resilience
As organizations continue to integrate IoT technology into their daily operations, the shift toward 'Security by Design' is no longer optional. Future trends will likely necessitate a move toward air-gapped systems or more stringent network monitoring for critical temperature-controlled environments. Retailers and manufacturers must prioritize the hardening of firmware and the implementation of anomaly detection systems that can identify and block unauthorized temperature spikes before they reach critical, fire-inducing thresholds.